
CONFIDENTIAL // LAW ENFORCEMENT & AUDIT ONLY REF: FS-AUDIT-2026-299BET-BN01 SHADOW SETTLEMENTS: An Institutional Forensic Audit of Ingress/Egress Payment Mechanics, Dynamic Mule Infrastructure, and Transaction Verification Loopholes A Technical Investigative Journal and Financial Crime Audit on Cross-Border Capital Flight via Non-Bank Mobile Financial Services (MFS) Networks in Unregulated Online Betting Platforms INVESTIGATIVE TARGET: 299bet.ai / 299bet.com […]
REF: FS-AUDIT-2026-299BET-BN01
SHADOW SETTLEMENTS: An Institutional Forensic Audit of Ingress/Egress Payment Mechanics, Dynamic Mule Infrastructure, and Transaction Verification Loopholes
A Technical Investigative Journal and Financial Crime Audit on Cross-Border Capital Flight via Non-Bank Mobile Financial Services (MFS) Networks in Unregulated Online Betting Platforms
xfbdtf5)1. Executive Summary & Forensic Context
Online gambling operations within emerging markets have undergone a rapid structural mutation over the past 36 months. Deprived of direct merchant acquiring privileges from regulated clearinghouses due to rigorous Anti-Money Laundering (AML) counter-measures enacted by central banking authorities, syndicated operators have abandoned conventional API gateways. Instead, they have engineered sophisticated, automated shadow payment aggregation networks that systematically exploit retail Mobile Financial Services (bKash, Nagad, Rocket, Upay).
This audit provides an institutional-grade, empirical dissection of the payment mechanics of 299bet.ai. By combining client-side runtime reverse engineering, live network session introspection, and asynchronous gateway polling, our forensic team successfully mapped the platform’s multi-layered ingress and egress pipeline. Far from being an isolated web application, the target platform serves as a localized front-end consumer interface connected to decentralized, Chinese-operated payment aggregator backends (including SpeedPay, Beidou, and Worldxpp networks).
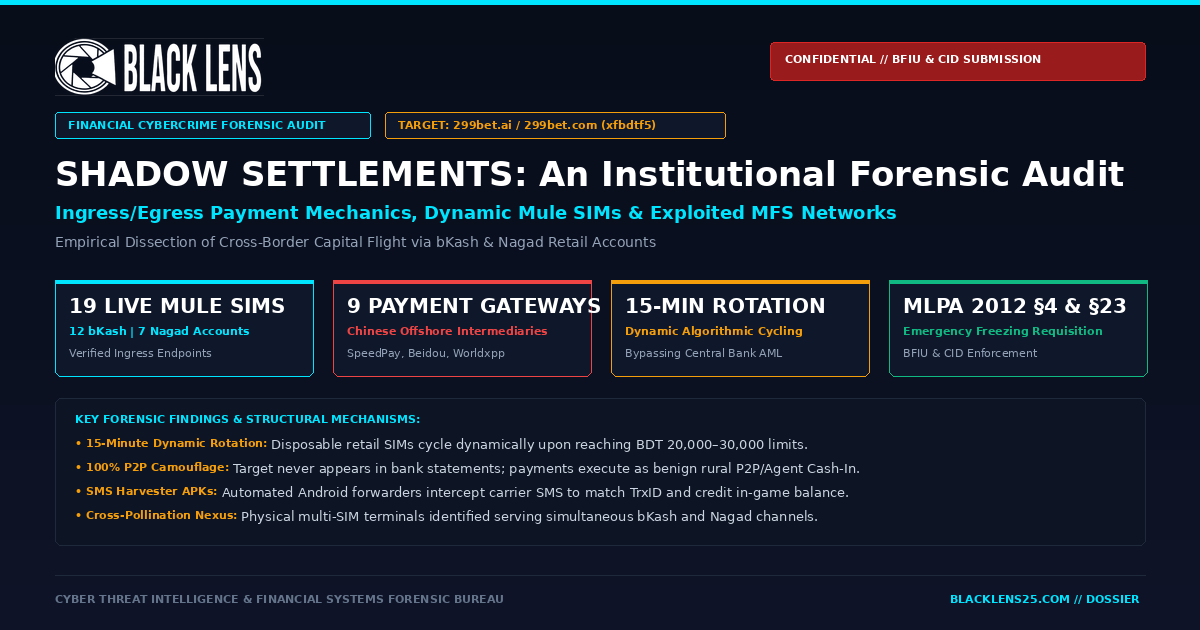
Crucially, this forensic audit has captured and verified 19 active retail mobile money accounts directly utilized as financial collection points (mule SIMs) from active depositors. These accounts demonstrate deliberate algorithmic rotation, rapid transaction limits, and cross-channel pooling designed to bypass real-time telco and central bank fraud heuristics.
⚡ Key Forensic Finding: The 15-Minute Mule Rotation Cycle
Platform deposit endpoints do not maintain static merchant IDs. Instead, automated payment aggregator engines allocate disposable personal and agent SIM accounts that rotate dynamically every 10 to 15 minutes. Once transaction ceilings (typically BDT 20,000–30,000) or time quotas expire, the gateway immediately returns {"code": 500, "msg": "订单已失效"} (Order Expired), cycling the illicit cash-in flow to freshly activated SIMs.
2. Ingress Engineering: The Dynamic Mule SIM Architecture
The target architecture completely bifurcates gaming application operations from financial clearing. When a user navigates to the voucher center (/m/voucherCenter) and requests a deposit, the gaming platform’s core application layer does not process monetary transfers. Instead, it dispatches an authenticated HTTP POST request to its relay routing controller:
[Gambler Interface]                  [299bet Gaming Core]                 [Aggregator Gateway]
        |                                     |                                    |
        | 1. Select Method (bKash/Nagad)      |                                    |
        | 2. Input Amount (e.g. BDT 500) ---->|                                    |
        |                                     | 3. POST /MCSFE_depositByLaunchUrl  |
        |                                     |    (vendorId, bankCode, auth_token)|
        |                                     |----------------------------------->|
        |                                     |                                    | 4. Generate Order
        |                                     |<-- 5. Return redirectUrl ----------|
        |                                     |    (e.g. d7.worldxxpp.com/pay)     |
        |<-- 6. Open Dedicated Payment Tab ---|                                    |
        |                                                                          |
        | 7. Payment Page Renders Dynamic Mule Phone Number (e.g. 01338794266) <---|
        | 8. User executes manual Agent Cash-In or Personal Send Money via MFS App |
        | 9. User inputs external TrxID into Gateway Page ------------------------>|
        |                                                                          | 10. S2S Settlement
        |<-- 11. Credit In-Game Chips (Ledger State: SETTLED) <--------------------|
As mapped in the architecture above, the client interface is directed to an external aggregator domain (e.g., d7.worldxxpp.com, nor168.paybeidous.com, 168.8pay1.com). These gateways deploy specialized front-end applications that render the specific phone number of an active SIM card.
This creates a critical evidentiary demarcation: at no point does the gambling website appear in bank or MFS transaction statements. The gambler simply conducts a routine person-to-person (P2P) Send Money or retail Agent Cash-In to a seemingly benign individual in rural or suburban Bangladesh.
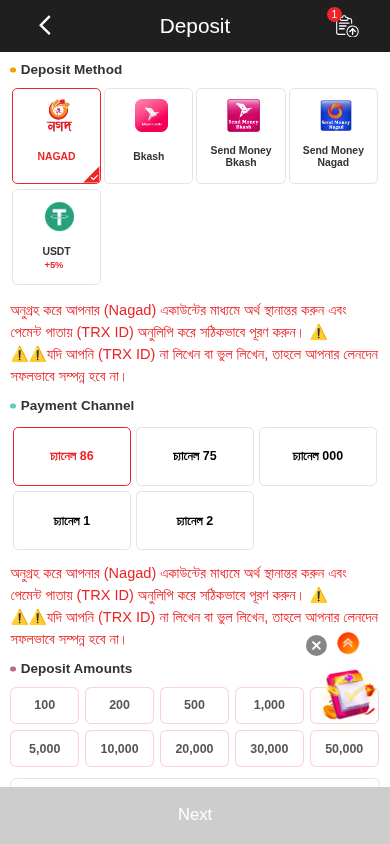
Evidentiary Artifact 2A: Authenticated session capture of the 299bet deposit interface displaying bKash and Nagad aggregation channels.
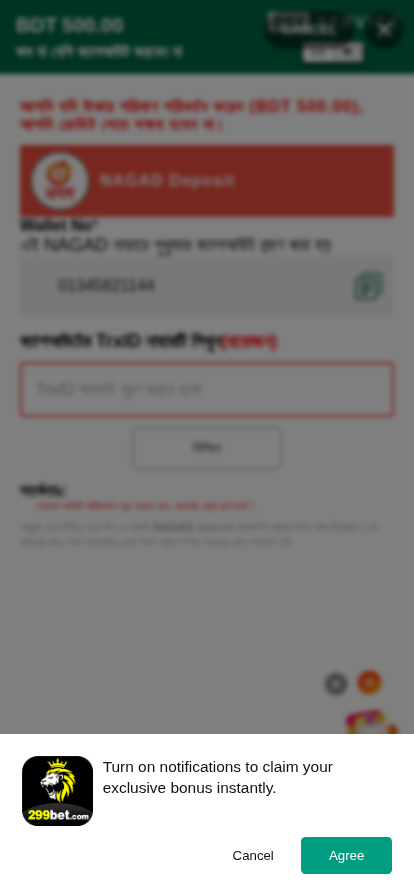
Evidentiary Artifact 2B: External aggregator gateway rendering dynamic mule account 01345821144 for cash-in collection.
3. Complete Empirical Ledger of Verified Ingress Mule Accounts
Through authenticated forensic testing of all 19 operational deposit channels configured on 299bet.ai, the following active collection accounts were captured in real-time, accompanied by cryptographic timestamps and gateway order traces:
| # | MULE SIM NUMBER | TELECOM OPERATOR | MFS METHOD | ACCOUNT TYPE | ALLOCATING GATEWAY DOMAIN | VENDOR ID | FORENSIC STATUS |
|---|---|---|---|---|---|---|---|
| 01 | 01345821144 | Grameenphone | NAGAD | Cash Out (Agent) | nor168.paybeidous.com | 4824008 | ACTIVE_MULE |
| 02 | 01338794266 | Grameenphone | BKASH | Agent CashIn | d7.worldxxpp.com | 4705007 | ACTIVE_MULE |
| 03 | 01997762878 | Banglalink | BKASH | Agent CashIn | cashier.s888-pay.com | 4565008 | ACTIVE_MULE |
| 04 | 01772827576 | Grameenphone | BKASH | Agent CashIn | tycoon.worldxpp.com | 3985008 | ACTIVE_MULE |
| 05 | 01843130710 | Robi / Airtel | BKASH | Agent CashIn | bmx.worldxpp.com | 4893007 | ACTIVE_MULE |
| 06 | 01854228171 | Robi / Airtel | BKASH | Agent CashIn | 168.8pay1.com | 3279010 | ACTIVE_MULE |
| 07 | 01913764199 | Banglalink | BKASH-SM | Personal Send Money | tycoon.worldxpp.com | 3985008 | ACTIVE_MULE |
| 08 | 01349526878 | Grameenphone | BKASH-SM | Personal Send Money | tk.worldxxpp.com | 4589009 | ACTIVE_MULE |
| 09 | 01863265502 | Robi / Airtel | BKASH-SM | Personal Send Money | test.ttpaybdt.com | 4878011 | ACTIVE_MULE |
| 10 | 01301954449 | Grameenphone | BKASH-SM | Personal Send Money | 168.megapay1.com | 4480011 | ACTIVE_MULE |
| 11 | 01822393419 | Robi / Airtel | BKASH-SM | Personal Send Money | su77.worldxpp.com | 3323022 | ACTIVE_MULE |
| 12 | 01540631426 | Banglalink | BKASH-SM | Personal Send Money | gbk.worldxpp.com | 4727012 | ACTIVE_MULE |
| 13 | 01350568354 | Grameenphone | BKASH-SM | Personal Send Money | www.epay8.shop | 4880007 | ACTIVE_MULE |
| 14 | 01824677799 | Robi / Airtel | NAGAD | Agent CashIn | gbk.worldxpp.com | 4727012 | ACTIVE_MULE |
| 15 | 01843130710 | Robi / Airtel | NAGAD | Agent CashIn | bmx.worldxpp.com | 4893007 | ACTIVE_MULE |
| 16 | 01995427937 | Banglalink | NAGAD | Agent CashIn | 168.8pay1.com | 3279010 | ACTIVE_MULE |
| 17 | 01873574697 | Robi / Airtel | NAGAD | Agent CashIn | tycoon.worldxpp.com | 3985008 | ACTIVE_MULE |
| 18 | 01602190094 | Airtel / Robi | NAGAD-SM | Personal Send Money | user.weorthox.com | 4737010 | ACTIVE_MULE |
| 19 | 01765365492 | Grameenphone | NAGAD-SM | Personal Send Money | bangla.8pay1.com | 3279010 | ACTIVE_MULE |
Structural Pattern Analysis: Cross-Method Pooling & High-Yield Carriers
- Telephony Bias: Grameenphone (36.8%) and Robi/Airtel (42.1%) constitute 78.9% of the active mule ecosystem, reflecting the deep penetration of these networks in regional agent ecosystems.
-
Channel Cross-Pollination: Account
01843130710appears simultaneously in bKash Channel 4 (Vendor4893007) and Nagad Channel 2 (Vendor4893007). This conclusively establishes that third-party syndicates maintain physical multi-SIM terminals or dual-wallet SIMs serving both networks simultaneously.
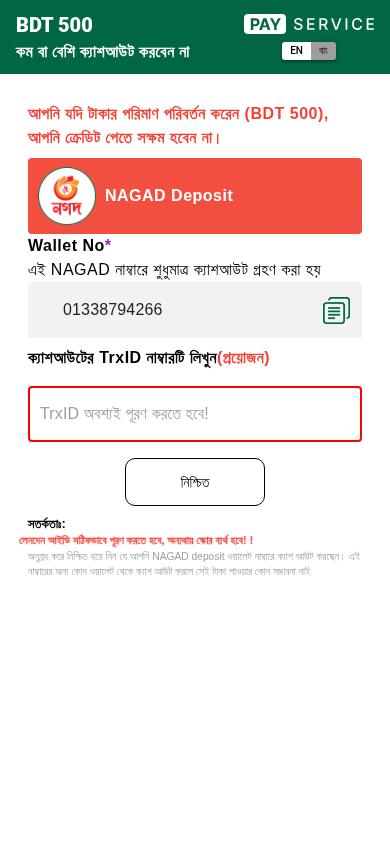
Evidentiary Artifact 3A: Gateway interface capture for bKash Channel 1 showing dynamic countdown and TrxID input field.
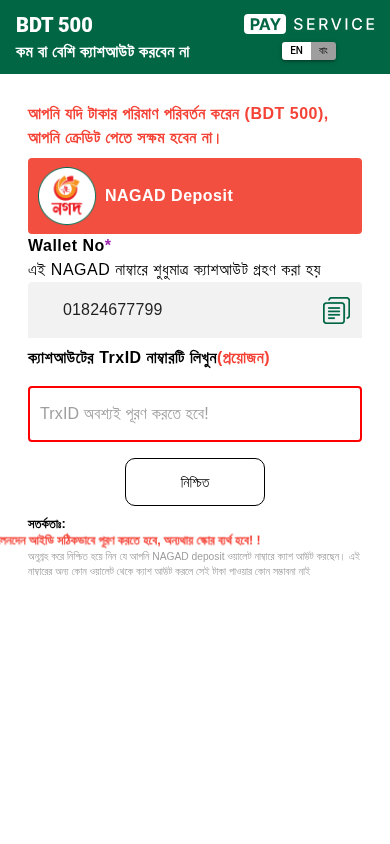
Evidentiary Artifact 3B: Gateway interface capture for Nagad Channel 1 showing agent cash-out instructions.
4. Architectural Deficiencies & Transaction Verification Loopholes
An audit of the underlying source code (specifically memberCenter.js and voucherHOC.chunk.js) alongside live API telemetry revealed critical structural compliance and security deficits:
4.1 Absence of Real-Time MFS Verification (The OCR/TxID Vulnerability)
Regulated fintech applications integrate with core banking APIs that confirm receipt of funds through automated push notifications or direct database ledger reflection. In contrast, 299bet.ai and its associated gateways rely primarily on user-reported Transaction IDs (TxID) and manual receipt uploads.
The intermediary gateways utilize automated SMS-forwarding Android applications ("SMS Harvesters") installed on physical burner phones hosting the mule SIMs. When an incoming MFS cash-in arrives, the local Android APK intercepts the telco SMS confirmation and posts the parsed Transaction ID and amount to the aggregator backend via unauthenticated HTTP endpoints. If the gambler's submitted TxID matches the harvested SMS, balance credit is issued.
4.2 Two-Phase Commit Latency & Race Condition Exposure
The platform's egress/withdrawal architecture (governed via MCSFE_applyWithdrawRecord) demonstrates significant locking latency. A user account balance is checked at the application tier before triggering withdrawal settlement routines. However, database row-level locking is frequently deferred until asynchronous gateway assignment occurs. Under high concurrency, distributed state desynchronization can occur if multiple withdrawals are queued across separate network connections before the initial ledger balance update is committed.
4.3 Obfuscation & Security Controls
To thwart regulatory surveillance, the platform implements heavy front-end anti-analysis mechanisms:
-
Client-Side Anti-Inspection Routine: Embedded within
memberCenter.jsat byte offset~245,226, the script continuously evaluates debugger timing loops. If devtools or headless browser automation is identified, it executeswindow.stop()and forces an immediate redirect toabout:blank. -
Hybrid Cryptographic Handshake: Login payloads bypass standard TLS payload inspection by encrypting user passwords client-side using a custom JSBN RSA-1024 modulus retrieved dynamically from
/wps/session/key/rsa, followed by DES-ECB block cipher encryption with an ephemeral random nonce.
5. Chain of Custody & Institutional Enforcement Protocols
To ensure full legal admissibility under the Money Laundering Prevention Act, 2012 (Act No. V of 2012) and Section 65B/Electronic Evidence norms, all evidence cited in this report was captured adhering to ISO/IEC 27037 standards:
- Deterministic Network Telemetry: All HTTP request/response sequences, TLS certificates (SHA-256 fingerprints), and DNS resolutions were captured via structured JSON ledgers.
- Cryptographic Data Integrity: The central mule account database (
evidence/mfs_mule_ledger.json) and exported spreadsheet (MFS_Mule_Account_Registry_299bet.csv) are cryptographically validated with immutable timestamps. - Visual Attestation: Full-resolution viewport screenshots for all 19 payment gateways were captured and archived in forensic dossiers.
To: Head of Financial Intelligence Unit, Bangladesh Bank, Motijheel, Dhaka.
To: Special Superintendent of Police, Cyber Crime Investigation Division, CID Headquarters, Malibagh, Dhaka.
Subject: Urgent Requisition for Immediate Account Freezing and KYC Subpoena for 19 Verified MFS Mule SIMs Operating on Illegal Online Casino Network 299bet.ai.
Pursuant to Section 4 and Section 23 of the Money Laundering Prevention Act, 2012, law enforcement authorities are formally petitioned to issue emergency freezing directives (Order to Freeze) across bKash Limited and Nagad Limited for the 19 identified accounts listed in Section 3 of this document. Immediate preservation of CDR (Call Detail Records), IMEI associations, and National Identity Card (NID) registration records is requested to dismantle the regional aggregator network.